Brevo login flaw enabled phishing email targeting 347K Trezor subscribers
Cointelegraph· Cointelegraph by Ezra Reguerra· Sep 11, 2026 · 4:21 AM

Trezor told Cointelegraph that the phishing email was sent to 347,000 subscribers and said it is treating every address as “known to the attacker and possibly reusable for phishing.”
This is a summary. Read the complete story at Cointelegraph below.
Read full article at CointelegraphRelated Stories
cryptoabout 3 hours ago
Canton’s CC rises 4% as SEC staff view it as ‘digital commodity’
SEC staff’s no-action letter covers CC earned by running infrastructure and applications, but is not a binding ruling on its legal status.
Cointelegraph
cryptoabout 4 hours ago
Binance hack may be ‘temporary setback’ for crypto, Grayscale’s Pandl says
Zach Pandl highlighted institutional custody safeguards as crypto markets recovered some losses following the record $6.3 billion Binance hack.
Cointelegraph
cryptoabout 4 hours ago
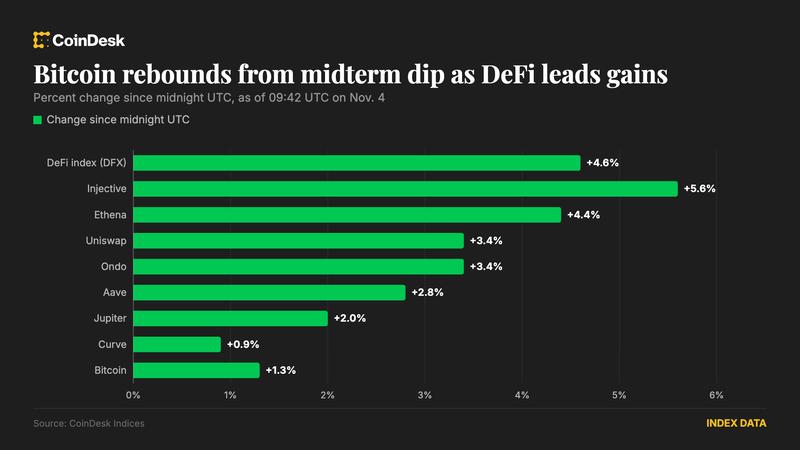
Bitcoin rebounds from midterm dip as DeFi leads gains
Bitcoin recovered from a dip to around $75,600 as Democrats won Congress, while DeFi tokens led gains and Trump-linked coins fell.
CoinDesk